
Sep 15, 2026, 2:29:58 PM Paul Breitenbach 12 min read

Your company just hit 80 employees, and the managed IT agreement you signed two years ago already has cracks. Tickets take longer, new hires wait days for full access, and security reviews happen once a year if they happen at all.
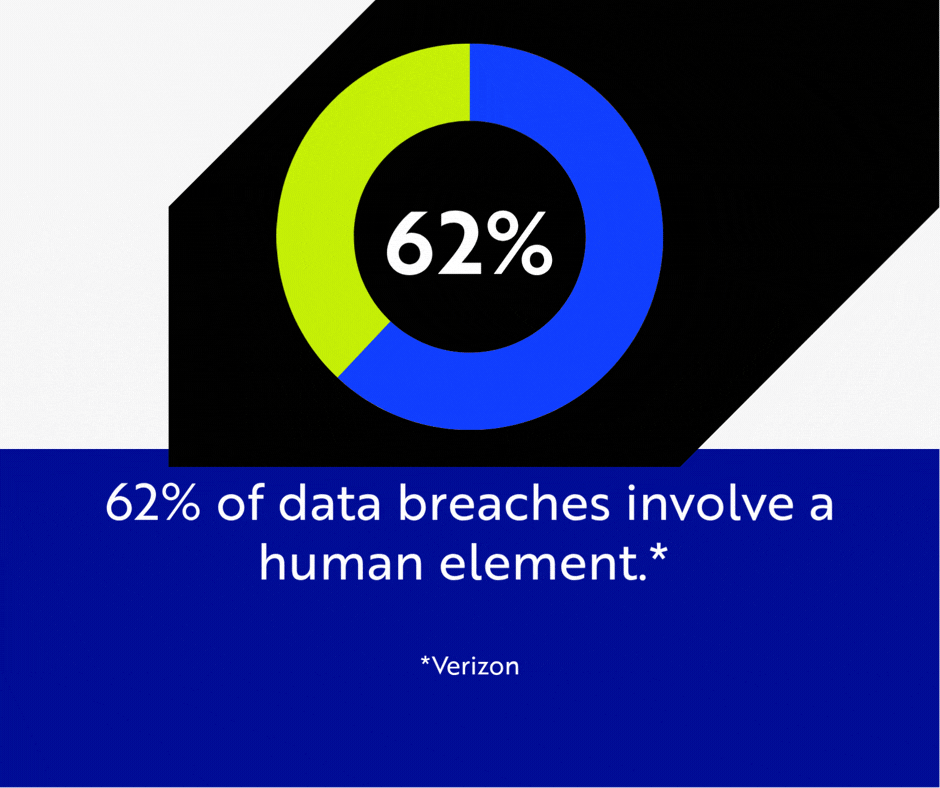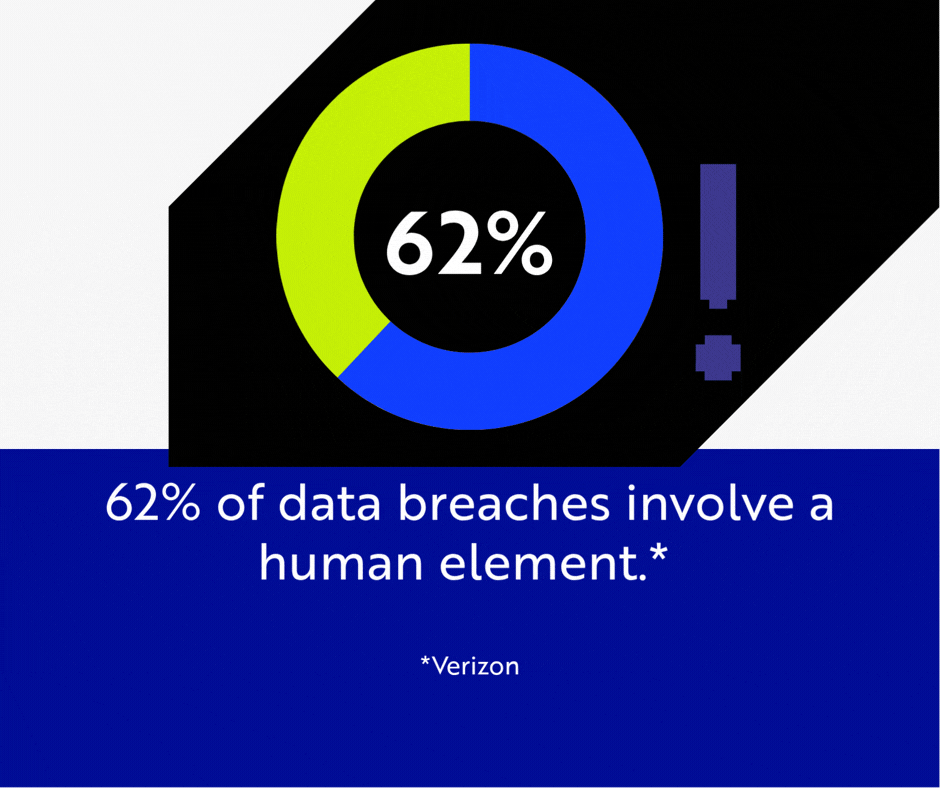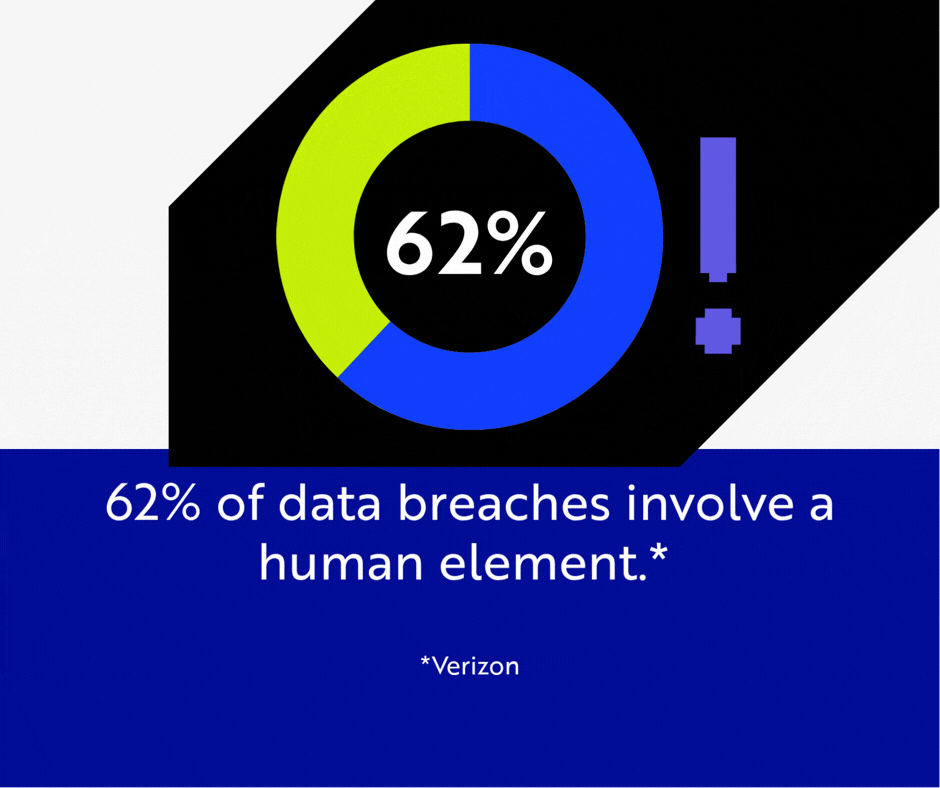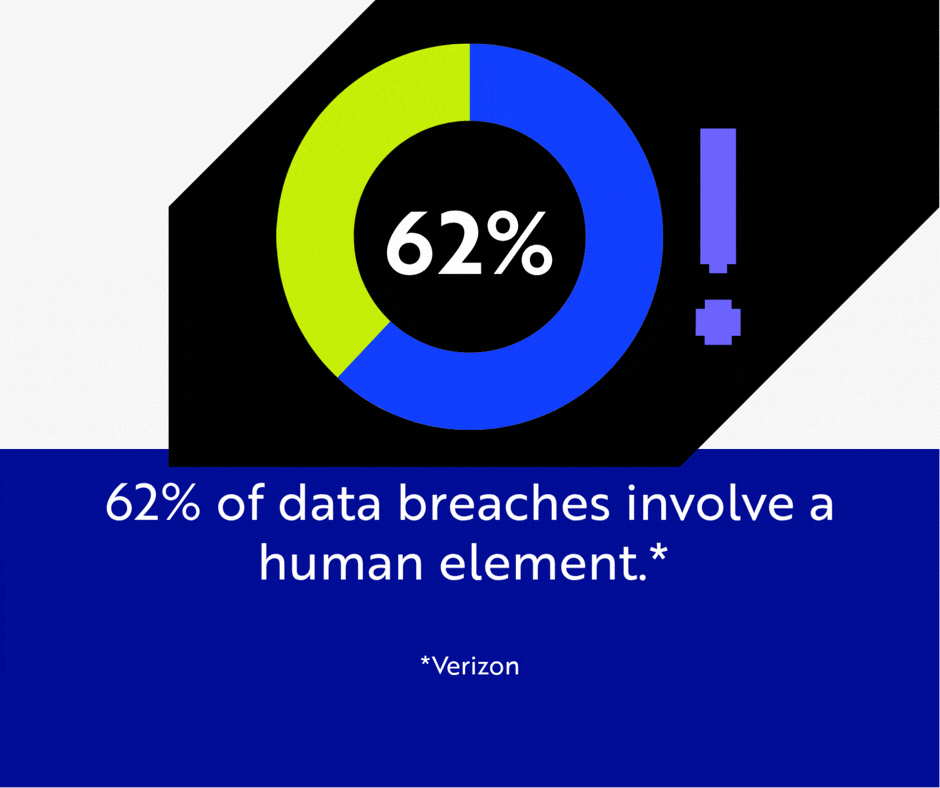
That slow erosion of IT reliability is predictable. Agreements built for a 50-person office rarely hold up at 120, let alone 200. The pressure is not only operational. Verizon's 2026 Data Breach Investigations Report analyzed more than 22,000 confirmed breaches, its largest dataset ever, and found the human element involved in 62% of them. Every new hire is a new person who can be phished, a new device that needs patching, and a new identity that needs to be revoked when they leave.
This article walks through the areas you should review before your next headcount milestone, so your IT agreement supports the business you are building rather than the one you have already outgrown. If you are still deciding whether to outsource at all, start with When to Outsource IT: Scaling In-House Teams in 2026 and Why One IT Guy Can't Do It All Anymore.
In this article
- Key Takeaways: What Growing SMBs Should Know About Scalable MSPs
- What Changes Between 80 and 200 Employees
- What to Evaluate in a Scalable Managed IT Agreement
- The Contract Redline Checklist
- How to Choose an MSP Agreement Built for Your Next 100 Hires
- FAQs About Scalable MSP Agreements
Key Takeaways: What Growing SMBs Should Know About Scalable MSPs
- A scalable MSP agreement includes clear terms for adding users, sites, and services without renegotiation.
- Security provisions need to grow alongside headcount, covering endpoints, identity, and network layers equally.
- Flat-fee, per-user pricing protects your budget from unpredictable spikes as your team expands past 100 employees.
- Provisioning and offboarding SLAs matter more at 200 employees than at 80, because every lingering account is a security gap.
- An annual agreement review and a clean exit clause prevent the gap between what you need and what you are paying for.
What Changes Between 80 and 200 Employees
The thesis of this article is simple: what worked at 80 will not work at 200. Here is what typically shifts along the way.
| 80 employees | 120 employees | 200 employees | |
|---|---|---|---|
| Endpoints to manage | 90–120 | 140–180 | 240–300+ |
| Locations | One office, some remote | Second site or growing remote team | Multiple offices, field teams, multiple time zones |
| Compliance scope | One framework, annual audit | Customer security questionnaires, cyber insurance requirements | Continuous compliance, formal evidence collection, possibly multiple frameworks |
| Support model | Shared helpdesk, best-effort response | Defined SLAs by priority | Tiered SLAs, after-hours coverage, regional field support |
| IT leadership | Owner or ops lead makes technology decisions | Part-time strategic input | vCIO with a 12–36 month roadmap and quarterly reviews |
| Hiring rhythm | A few hires per quarter | Several per month | Cohorts of new hires, sometimes weekly |
Each row is a place where an agreement written for the left column starts to fail in the right column.
What to Evaluate in a Scalable Managed IT Agreement
1. Pricing and Headcount Flexibility
A scalable agreement lets you add users and devices without triggering a full contract renegotiation. Look for per-user pricing with defined add-on tiers, so onboarding 20 new employees does not require a procurement cycle.
Ask your provider how they handle mid-contract changes. If the answer involves custom quotes for every adjustment, your agreement was built for a static headcount.
Then look at what sits outside the monthly fee. Emergency support, after-hours incidents, and project work are the usual culprits behind surprise invoices. If those costs are billed separately, budget predictability disappears the moment something breaks on a Friday afternoon. A flat-fee, per-user model means your IT spend grows at a known rate as you add headcount, which lets you forecast IT with the same confidence you forecast payroll. Compass structures fully managed IT around fixed monthly per-user costs for exactly this reason.
For a broader look at where IT budgets leak during growth, see IT Cost Optimization for Small Businesses.
2. Service Scope That Matches Your Growth Trajectory
At 80 employees, you might only need helpdesk and basic monitoring. By 150, you will likely need cloud infrastructure management, compliance support, and structured security operations.
Review your agreement's service catalog against a realistic 18-month projection of your business. If your MSP does not offer cybersecurity, compliance advisory, and strategic IT planning under the same contract, you will end up coordinating across multiple providers. That coordination cost is real, and it shows up in lost time and accountability gaps.
13 Fully Managed IT Services Regulated Teams Need in 2026 breaks down what a complete service catalog should include.
3. Security Provisions That Scale with Endpoints
Every new employee adds at least one endpoint, one identity, and one potential attack surface. Your MSP agreement should specify how security coverage expands as headcount increases.
The stakes keep rising. IBM's 2026 Cost of a Data Breach Report puts the global average cost of a breach at $4.99 million, a 12% increase over the prior year and a record high, and reports a 56% increase in AI-driven attacks led by deepfake impersonation and AI-enabled malware. The same report found that organizations making extensive use of AI and automation in their security operations saved $1.93 million per breach compared with those using none. That is the strongest financial argument for insisting that detection and response tooling be built into your agreement rather than sold as an add-on.
The way attackers get in has changed, too. For the first time in the DBIR's 19-year history, exploiting known software vulnerabilities overtook stolen credentials as the top initial access vector, accounting for roughly 31% of breaches. That makes patch SLAs a security provision, not just a maintenance detail.
Look for endpoint detection and response (EDR), identity protection, managed detection and response (MDR), and defined patching windows as standard coverage. Compass builds multi-layered defense into its Core Defense and Apex Security tiers, so protection grows alongside your workforce.
For the executive view of what a breach actually costs a mid-sized company, read Cost of a Cyber Breach: A CEO's Guide.
4. vCIO and Strategic Advisory Access
An MSP that only fixes tickets will not help you plan for your next 100 hires. A vCIO aligns your technology roadmap with your business goals, reviewing infrastructure investments on a 12 to 36-month horizon.
Before signing or renewing, confirm that strategic advisory is included, not billed separately as a project. Then ask what a quarterly business review actually contains. A useful QBR covers ticket trends and root causes, security posture and open risks, license and asset utilization, upcoming lifecycle replacements, and a rolling budget forecast tied to your hiring plan. If your provider's QBR is a slide of ticket counts and a renewal pitch, that is not strategic advisory.
The vCIO Advantage explains how to measure the return on that role, and The Case for an Annual Technology Plan shows what the planning output should look like.
5. Compliance Readiness for Regulated Industries
If you operate in healthcare, financial services, or manufacturing, your compliance obligations intensify as you grow. The agreement should define who owns audit preparation, evidence collection, and compliance documentation.
The cost of getting this wrong is highest in regulated sectors. IBM's 2025 report found healthcare had the highest average breach cost of any industry for the 14th consecutive year, at $7.42 million, and that U.S. breaches averaged $10.22 million, driven in part by regulatory penalties. NIST's Cybersecurity Framework 2.0 added a Govern function specifically because organizations that treat security and compliance as separate, once-a-year activities carry more risk than those that embed them into operations.
A provider that treats compliance as a separate engagement will leave gaps between your IT operations and your regulatory requirements. See What Managed IT Services Cover for Compliance and Managed IT for Cybersecurity Compliance in 2026 for what to expect from an integrated model.
6. User Provisioning and Departure Processes at Scale
At 80 employees, a three-day setup window for a new hire might be acceptable. At 200, it is a bottleneck. Your agreement should define SLAs for provisioning accounts, devices, and security access on day one.
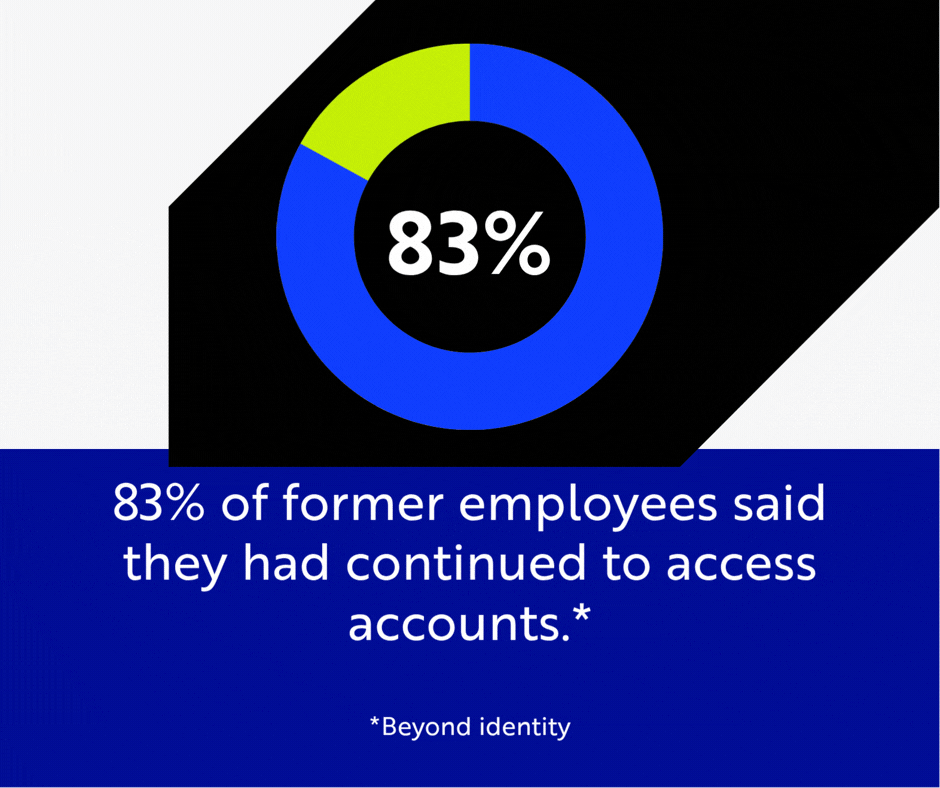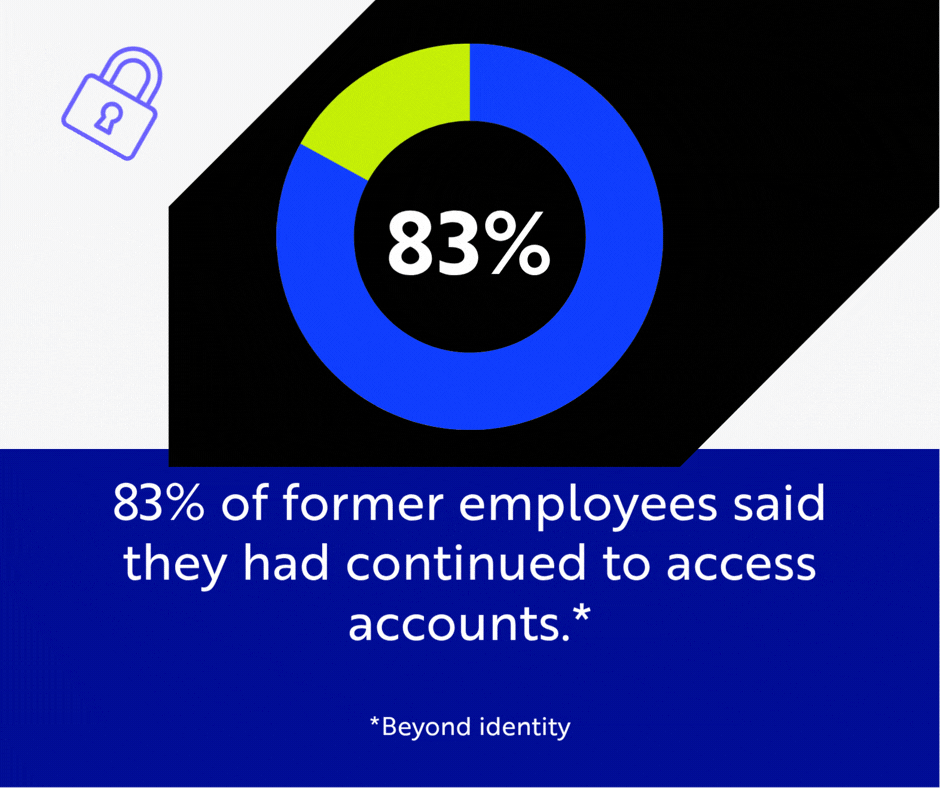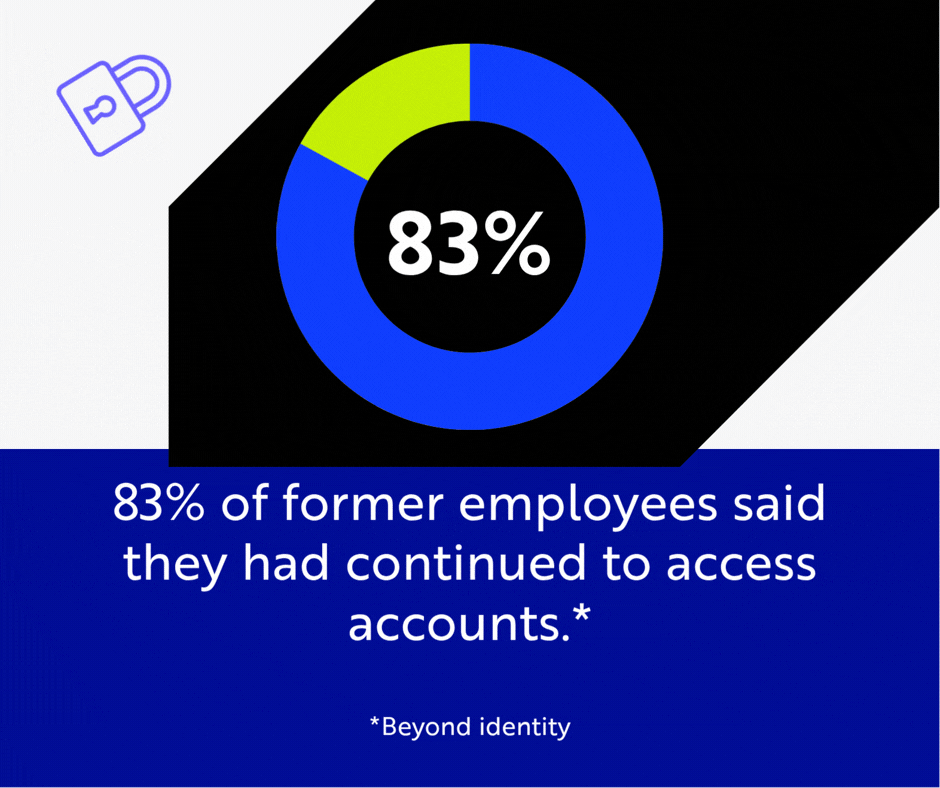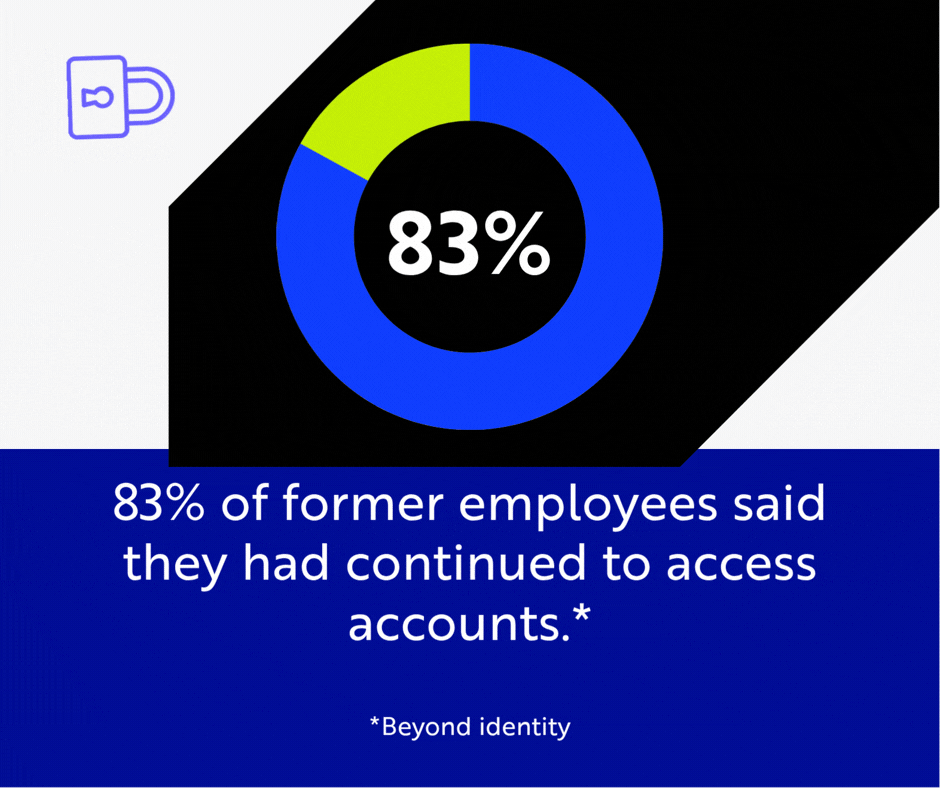
The offboarding side carries equal weight, and the data here is uncomfortable. In a Beyond Identity survey of more than 1,100 employees and business leaders, 83% of former employees said they had continued to access accounts belonging to a previous employer after leaving. An earlier OneLogin survey of 500 U.S. IT decision-makers found that a quarter of organizations took more than a week to fully de-provision a departing employee, and 20% said a failure to de-provision had contributed to a data breach at their organization.
A structured departure process should revoke credentials, recover assets, and update your security posture the same day. Your agreement should name a specific window, not "promptly." 10 Essential SLAs for Multi-Site Outsourced IT Support covers the provisioning and response SLAs worth writing into the contract.
7. Support Model That Covers Your Geography
A 200-person company often spans multiple offices, remote workers, and field teams. Your MSP agreement needs to specify how support is delivered across those locations, whether through remote resolution, regional field engineers, or both.
Compass combines a 100% U.S.-based support team with regional field engineers, so employees get the same response time in a satellite office as they do at headquarters. That consistency matters when you are hiring across time zones.
15 Outsourced IT Services for Multi-Location Offices outlines what multi-site support should include.
8. Communication Infrastructure That Grows with You
Your next 100 hires will need phones, video conferencing, and messaging at scale. If your MSP agreement does not address unified communications, you will manage a separate telecom relationship, a separate vendor contract, and a separate set of accountability gaps.
Consolidating voice, video, messaging, and contact center operations under the same team that manages your IT and security environment keeps communication from becoming another disconnected line item. The eBook From Dial Tone to Differentiation covers how to approach that consolidation.
9. Annual Agreement Reviews and Exit Clauses
If your current provider resists formal reviews, that resistance tells you something about their confidence in their own service delivery.
A good MSP agreement includes a structured annual review where both parties assess performance against documented benchmarks. If your current provider resists formal reviews, that resistance tells you something about their confidence in their own service delivery.
Equally important: review the exit clause. You should be able to move to a new provider without a data hostage scenario. Your agreement should guarantee access to your documentation, credentials, configurations, and environment data at termination, and it should define a transition period during which the outgoing provider cooperates with the incoming one. Some organizations go further and require that documentation and administrative credentials be held in a shared or escrowed location throughout the engagement, so nothing has to be "handed over" at all.
The exit clause also matters if your provider is the one that gets breached. Your IT Provider Was Breached: What to Do in the First 24 Hours walks through that scenario.
The Contract Redline Checklist
Before signing or renewing, confirm each of the following appears in the agreement in specific, measurable language. If a clause is missing or vague, ask for it in writing.
- Add-on user pricing schedule. Per-user cost for additional seats, with any volume tiers defined, and no requirement for a new quote below a stated threshold.
- New site onboarding terms. What it costs and how long it takes to bring a new office or remote cohort under the agreement.
- Provisioning SLA. A specific window for account, device, and access readiness for new hires, measured from request date.
- Offboarding SLA. A specific window for credential revocation and asset recovery, measured from notification.
- Security coverage definition. EDR, identity protection, MDR, and patching windows listed as included services, with the scope stated per user or per device.
- After-hours and emergency billing. Whether these are inside the monthly fee, and if not, the rate and the trigger.
- Strategic advisory inclusion. vCIO time and quarterly business reviews listed as included, with the QBR contents defined.
- Compliance ownership. Who prepares audit evidence, maintains documentation, and responds to customer security questionnaires.
- Annual review obligation. A required review against documented benchmarks, with a right to renegotiate scope at defined headcount milestones.
- Data and documentation return. Full return of documentation, credentials, and configuration data at termination, with a defined transition period and cooperation obligation.
For the full evaluation framework, download the MSP selection checklist.
How to Choose an MSP Agreement Built for Your Next 100 Hires
Your MSP agreement should be a growth document, not a maintenance contract. If it does not address headcount scaling, security expansion, compliance ownership, and strategic advisory, it will hold your business back before your next hiring push.
CompassMSP builds managed IT agreements around the way mid-market businesses grow, aligning IT, cybersecurity, cloud, and compliance under one accountable team. For a deeper look at the RFP questions and SLAs to bring to that conversation, read How to Choose a Fully Managed IT Provider in 2026.
The right direction starts with a technology partner who follows through. Schedule a consultation to review your current agreement against these criteria.
Paul Breitenbach
With nearly 20 years of experience designing enterprise-grade IT solutions, Paul specializes in supporting organizations that cannot afford downtime. Before becoming our CIO, he served as CIO of WorldwideIT, a Compass company, where he led large-scale infrastructure, cloud, and security initiatives for highly regulated industries.