
Sep 28, 2026, 4:07:47 PM Paul Breitenbach 13 min read

Every deal team knows how to audit a balance sheet. Few know how to run M&A IT due diligence with the same rigor, and that blind spot comes with a high price.
A target can appear clean on the surface while carrying years of deferred IT investment, security gaps, and expensive contracts. Those issues rarely stay confined to the IT budget. Technology risk hides in a different place, and by the time it surfaces, the buyer already owns it and the cost to fix it.
This doesn’t mean you have to hire an army of engineers to pore over source code. It's a case for asking sharper questions earlier in the deal process.
In this article
- The Ten Questions:
-
1. What will the technology cost to run after the transaction closes?
-
3. Does the actual cybersecurity posture match the written policies?
-
4. What is the level of compliance risk, and what would remediation cost?
-
5. Who holds the administrative keys and critical system knowledge?
-
6. What restrictive software licenses and vendor contracts come attached to this deal?
-
7. Can the current IT infrastructure scale to support growth?
-
9. Is there a disaster recovery and business continuity plan?
-
- Frequently Asked Questions
The Cost of Skipping IT Due Diligence
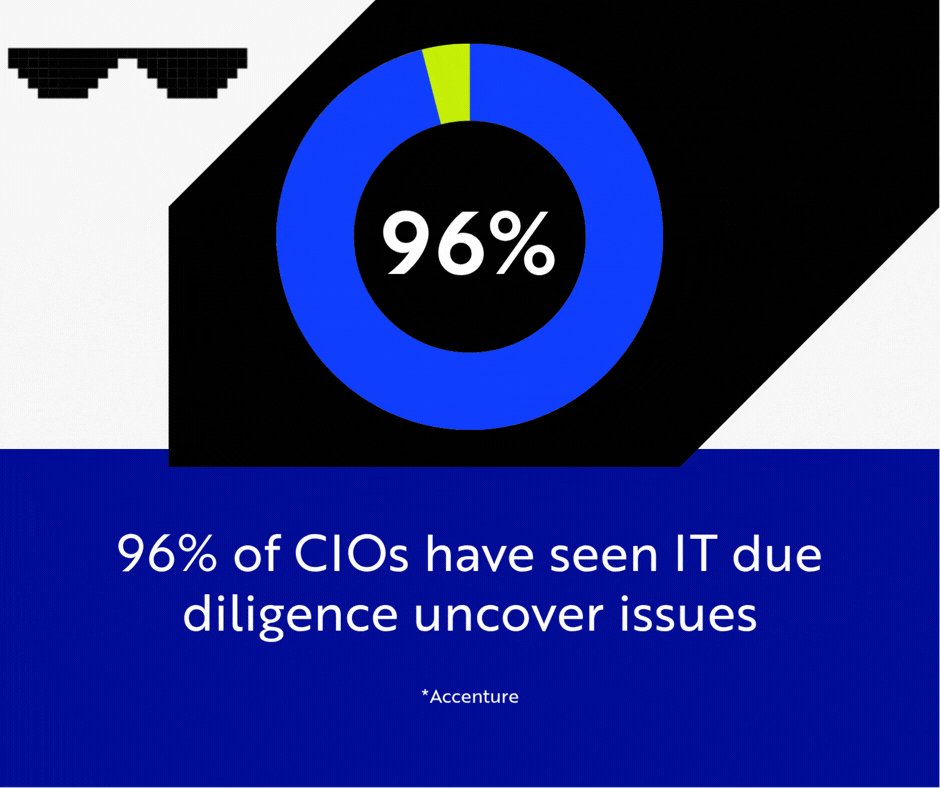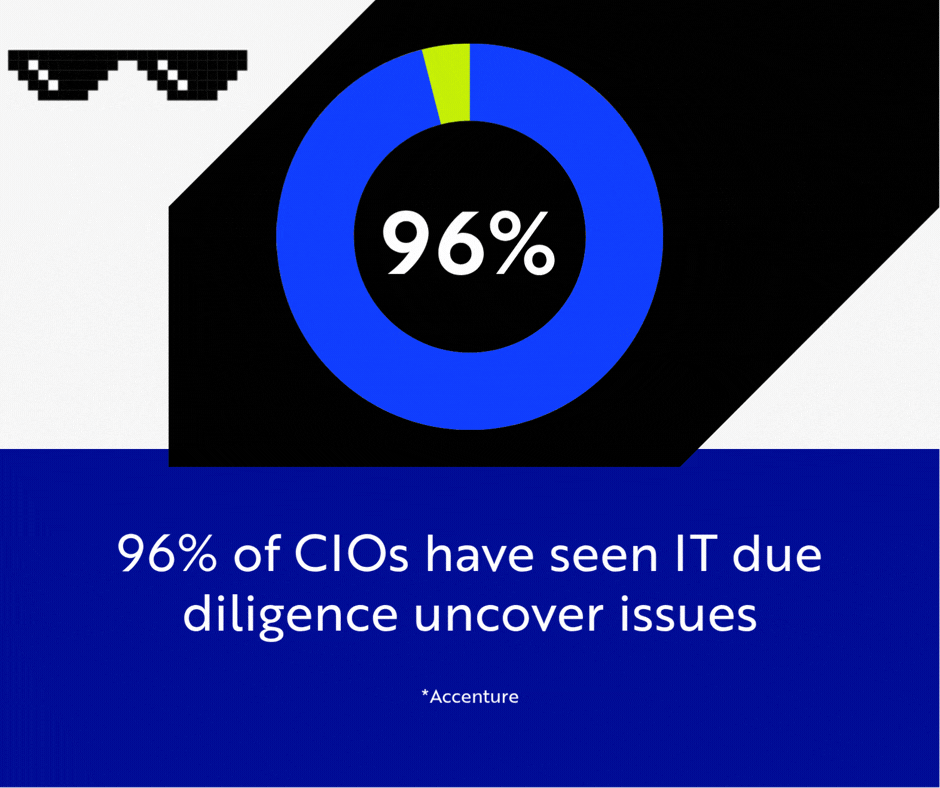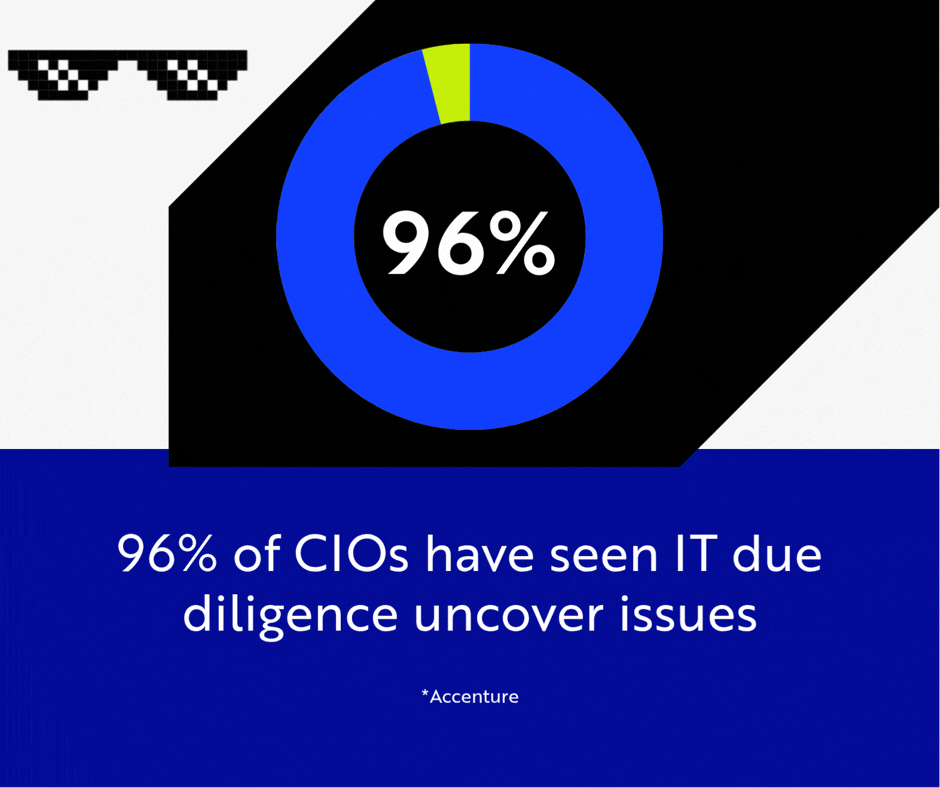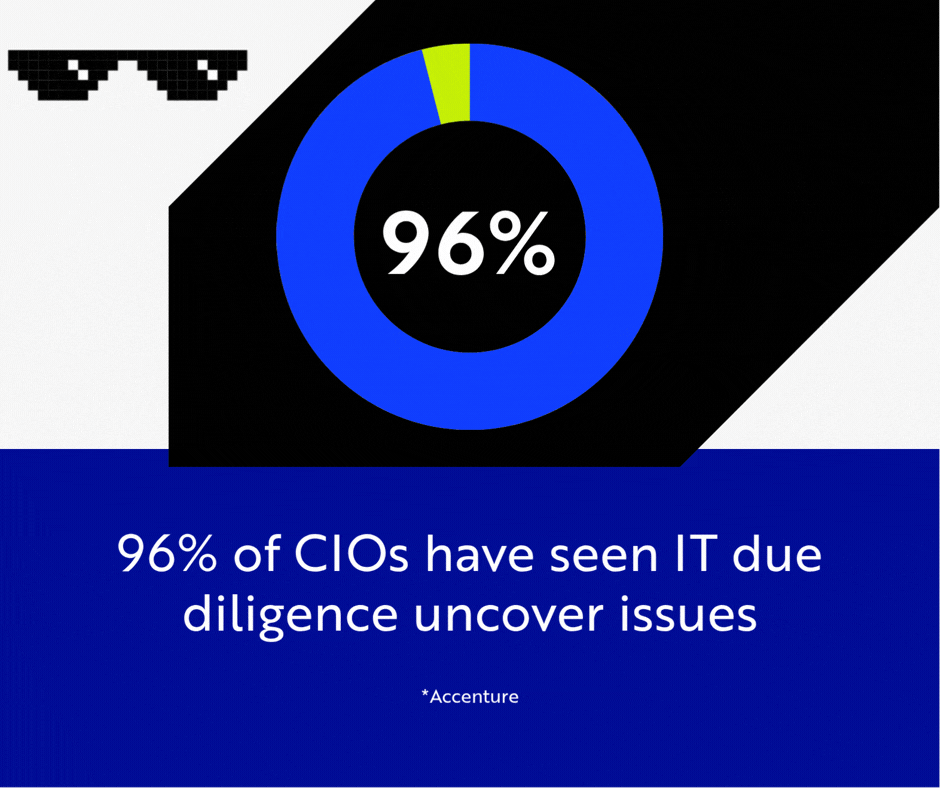
Technology and finance aren't separate conversations in a modern transaction. IT due diligence for private equity bridges the gap by answering financial questions instead of just technical ones. Accenture found that 96% of CIOs have seen IT due diligence uncover issues that materially affected a transaction. Skipping this work carries a massive financial setback.
CFOs and PE operators don't need to understand every server, application, or firewall. They need to know what the technology environment will cost, where it can break, how fast it can integrate, and whether it can support the investment thesis.
The ten questions below get you there; no technical background required. Each one connects an IT issue to a financial consequence and gives you hard data to bring to the negotiating table.
1. What will the technology cost to run after the transaction closes?
A company keeps costs artificially low by delaying hardware replacements, running unsupported software, or relying on a single employee to handle critical technology work outside their formal role. This strategy makes historical EBITDA look better, but it does not make those deferred costs disappear.
Ask what it will take to operate the business at an acceptable level after close, and separate recurring operating expenses from one-time remediation and IT integration costs.
Skeletons in the Server Closet: How to Identify Hidden IT Costs Before Close
Then ask a much harder question: What is missing from the current budget that you will have to fund? Look for redundant software licensing, unused cloud usage fees, and overlapping vendors. The target company shifts these hidden costs directly onto whoever owns the business next. Deloitte warns that buyers make incorrect assumptions about IT costs when diligence lacks depth, which ultimately damages the final purchase price.
2. How much technical debt are we inheriting?
Every system running on outdated software or a custom workaround nobody documented adds up. Roughly 40% of infrastructure systems carry some form of technical debt, and in an acquired company, that debt transfers with the deal.
Demand the target to quantify their technical debt. Require hard estimates on the exact cost and timeline to modernize their core systems. A vague answer is your answer. Undisclosed technical debt drains cash after the close.
This hidden debt surfaces during integration instead of during negotiation, leaving you with zero power to adjust the purchase price. M&A IT due diligence should identify what needs attention immediately, what can wait, and what the remediation will cost.
3. Does the actual cybersecurity posture match the written policies?
The disconnect between a documented security policy and what's actually happening creates massive breach risk. You inherit that legal and financial liability the moment the deal closes.
You need forensic proof that the target network is clean. A compromised technology environment requires expensive rebuilds, so you must find active threats before you assume the risk.
A Security Gap Is a Red Flag with a Heavy Price Tag
Push past basic cybersecurity checklists and demand forensic evidence: recent penetration test results, patch management schedules, incident response times. If the target can't produce them, that absence is your finding.
Cybersecurity vulnerabilities inside the acquired business can spread to the entire portfolio during integration, triggering immediate remediation costs and damaging your cyber insurance position.
4. What is the level of compliance risk, and what would remediation cost?
Industry mandates like HIPAA, PCI DSS, or CMMC represent strict legal boundaries. When you acquire a company with unaddressed gaps, you inherit the legal obligation to report their past failures. This exact regulatory risk causes over 34% of dealmakers to walk away from potential acquisitions, according to KPMG. You must secure the target's compliance data before you assume that liability.
Demand a complete list of applicable regulatory frameworks, and request official audit reports to confirm their active controls satisfy government auditors. Then, put a precise number on every gap. A missing control tied to a $500,000 remediation project gives you the hard data needed to adjust your purchase offer.
5. Who holds the administrative keys and critical system knowledge?
Plenty of smaller and mid-market companies run on IT infrastructure that only the one IT person understands. This creates a dangerous key-person dependency. If that person leaves during or after the transition, operational continuity leaves with them. In other cases, a third-party vendor controls the entire environment instead. That provider may have weak service levels or no formal agreement.
Control over the network remains entirely non-negotiable. Ask who holds administrative credentials, who has access to critical systems, and where that documented knowledge lives. You also need to map out all access rights during the initial diligence phase. This early discovery prevents rogue access and secures your newly acquired asset.
6. What restrictive software licenses and vendor contracts come attached to this deal?
Long-term vendor agreements frequently conceal massive financial liabilities. A target may hold a multi-year contract for an outdated service or pay for overlapping vendors that inflate the true IT run rate. You inherit these terrible deals the moment the transaction closes.
IT due diligence should surface every active technology contract. Request a full inventory of software licenses, vendor contracts, and any change-of-control clauses buried in the fine print. This is exactly the kind of detail that's easy to miss in a fast-moving deal and expensive to discover afterward. The CFO should leave diligence knowing which agreements transfer cleanly and which require renegotiation.
7. Can the current IT infrastructure scale to support growth?
A platform strategy depends on IT infrastructure that can grow without a proportional jump in cost. Systems built for a standalone company of one size don't always hold up once that company becomes part of a larger portfolio.
Ask what would break first under increased volume, additional locations, or a merged user base. More than half of anticipated deal synergies are enabled by technology, so infrastructure that can't scale creates IT problems and caps the upside the deal was built around.
A network built for fifty employees collapses under the weight of two hundred. The target company’s current IT systems must support this planned growth.
8. What are the IT integration costs after the acquisition?
Deal teams consistently underestimate technology integration expenses when building their initial financial models. Financial projections often assume a rapid combination of assets, but boots-on-the-ground execution looks quite different. It involves migrating massive databases, mapping secure user access, and consolidating redundant software.
Technology alone accounts for 19% of one-time integration costs, according to Deloitte research, and the longer integration drags on, the less likely the organization is to hit the deal's strategic rationale and cost targets. You must get a realistic estimate of IT integration costs, level of effort required, and the approximate timeline.
9. Is there a disaster recovery and business continuity plan?
A target company often owns a basic backup solution but completely lacks a formal, tested recovery process. Cover your bases by asking what happens if a server fails, a ransomware attack hits, or a critical vendor goes dark for a week.
Request the exact date of their last disaster recovery test and their proven recovery time objective. A business that can't get back online quickly after an incident carries risk that doesn't appear anywhere in the financials until a crisis hits.
A company keeps costs artificially low by delaying hardware replacements, running unsupported software, or relying on a single employee to handle critical technology work outside their formal role. This strategy makes historical EBITDA look better, but it does not make those deferred costs disappear.
Ask what it will take to operate the business at an acceptable level after close, and separate recurring operating expenses from one-time remediation and IT integration costs.
10. What's the honest timeline and cost of Day 1 readiness?
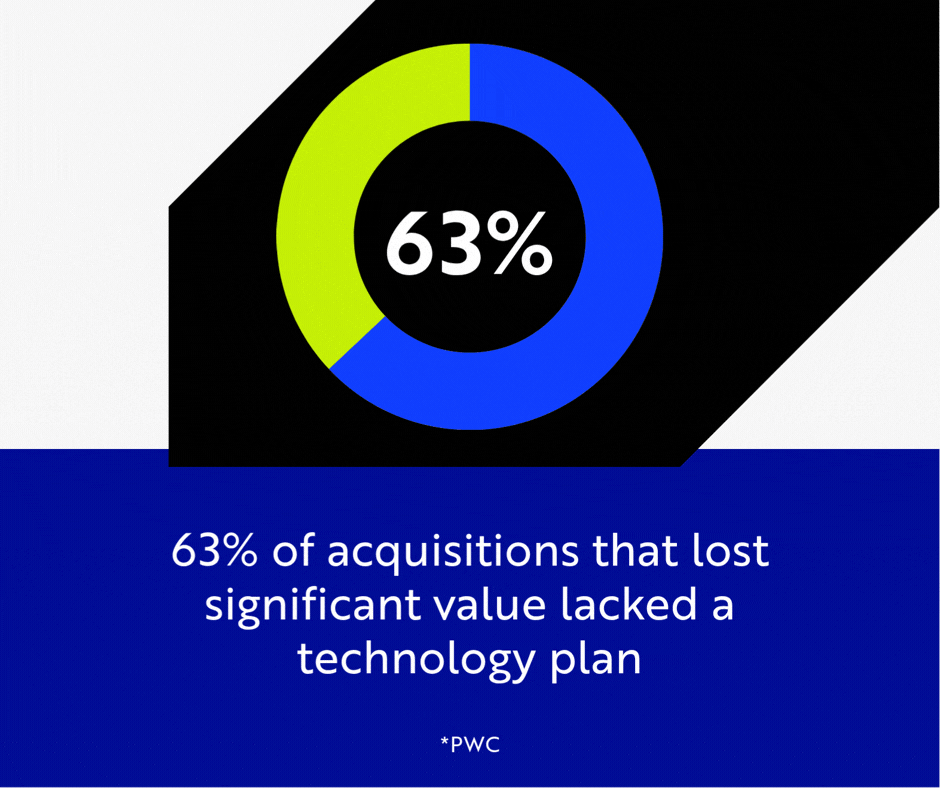
Day 1 readiness sounds basic, but it’s frequently the most underplanned part of the entire transaction. PwC found that 63% of acquisitions that lost significant value lacked a technology plan at signing.
Demand a specific Day 1 plan: what needs to happen, what it costs, and who owns it. If nobody can answer that clearly, that's a strong signal that IT due diligence hasn't gone deep enough yet.
Technology Due Diligence: The Fine Print of M&A Success
These IT due diligence questions will not guarantee a flawless integration. They do, however, ensure you price technology risk directly into the deal instead of absorbing a massive post-close surprise.
Your findings shape the final purchase price and deal terms before you commit capital. Pre-sale data dictates post-sale success. KPMG reports that 64% of private equity dealmakers rank integration due diligence among their top priorities.
Thorough technology due diligence maps out your integration strategy. You can prepare the necessary capital and deploy the right technical resources ahead of time, letting you control the acquisition’s narrative from the beginning.
Move Fast Without Flying Blind
In 2025, just 20 large deals accounted for one-third of total U.S. deal value. Deloitte predicts this is a sign that small- and mid-size transactions could present meaningful opportunities for corporate and PE buyers and sellers prepared to act in 2026. You must move quickly to capture these opportunities, and fast execution requires precise information.
Internal IT teams rarely possess the bandwidth to conduct a deep M&A audit. You need an external IT due diligence partner to translate complex technology flaws directly into hard financial numbers you can use at the negotiation table.
Execute the M&A Playbook with A Proven Partner
As a PE-backed, acquisition-driven operator, Compass has run this exact playbook from the inside and brings that experience to due diligence, integration, and everything that follows once the transaction closes. Our strategic vCIOs and vCISOs step into the deal room to evaluate the target environment end-to-end. We uncover hidden IT costs, identify compliance gaps, and build a concrete Day 1 integration plan.
Reach out to learn how we protect your capital so you can execute the transaction with total confidence.
Paul Breitenbach
With nearly 20 years of experience designing enterprise-grade IT solutions, Paul specializes in supporting organizations that cannot afford downtime. Before becoming our CIO, he served as CIO of WorldwideIT, a Compass company, where he led large-scale infrastructure, cloud, and security initiatives for highly regulated industries.